- Site menu:
- Latest Discussions
- Latest Newswire
- Archives
- Submit Story
- Story HOWTO
- Syndicate
- E-mail Alerts

Linux Malware: Should we be afraid?
The Password bluesBesides, most of my year-old passwords aren't that secure anymore either, according to ArsTechnica's most excellent article Why passwords have never been weaker and crackers have never been stronger. Main take-home message from the article: Any password less than 9 characters is easy to crack within an hour with, well, for "gamers" modest hardware. And to make things even more miserable, lots of websites 'fooled up' security. In fact lots of even bigger websites cannot be trusted with our passwords. Any password shorter than 9 characters you store on a website, once that website is cracked - should be considered vulnerable to 'reverse-lookup'. Where reverse-lookup means: Even if your password is not saved in plain text, the attacker can regain it from the hash by brute-forcing using General Computing on GPU's (GPGPU's) with programs written using OpenCL or NVidia's CUDA. This means if one website is hacked, all your other accounts with the same login / password should also be considered breached.This all puts a question mark above my head (you see it, huh?) concerning the security of my actions on my Ubuntu-desktop these days. The ultimate malware-kit?To put it in some context:Though a malware-kit for Linux is available, there are no exploits - yet. For Windows it's pretty easy to buy an exploit kit - you can almost buy them in the supermarket next to the groceries in the discount corner, while for Linux it isn't that simple. However, once an exploit for Linux is found, it's really dangerous as the attackers can just install one package on your OS which takes care of everything. That is, not only sniffing for bank credentials, but also trying to block safety-updates. They try to do so via DNS / host blocking, and the kit even has SOCK5-proxies on board and software-attempts to break outside sandboxes. So, let's say if in the past if a Linux exploit was found, it would have been much work to use that exploit to do malicious things. Now, however, after the exploit has been found, there's a high level of automation available to the malicious attacker. They can sit back, relax while zipping a coffee or vodka and their malware kit will be doing all the hard and daunting work. Of course, we could discuss if Linux is inherently more secure than Windows, given metrics such as severeness of security flaws and days to patch, such as SJVN does. Also, we could say: "My bank doesn't use username / password login, they use a token and two-way authentication. So even if my login and pass has been found, they cannot steal my money". But that's not what keeps my mind busy at the moment. What keeps my mind busy is: How easy is it for a cracker to change the DNS-system in my router, so that they can try to 'resolve' the name of my bank to _their_ IP? Why is it 99% of the Linux-routers in the world will never be updated? Why is Andoid so seemingly insecure - and may I add buggy and irresponsive, even if it has a Linux-kernel? Are there any user-friendly Android-alternatives which are more secure and work on my telco's network? What about _me_ and _you_?What if Ubuntu has an exploit and if people put the mentioned Hand-of-Thief malware on my or your PC? Will we notice? Will the malware-kit be able to send our name and bank account number to Russia? Now, true, LXer-readers - at least those who post opinions and discuss in the forum - are usually quite Linux-savvy. But contrary to some (I hope most) of them, I have to confess, I don't have intrusion detection or rootkit scan-schemes. OK, I ran both OpenBSD and Hardened Gentoo and hardened-gcc in the past, but nowadays I'm lazy and just use Ubuntu. Also, besides being lazy, using Ubuntu helps me help new Linux-users, as lots of those are on Ubuntu. That means, for all I know, my binaries are the same as for other people who use Ubuntu, unlike in my past "Gentoo-days".All of this leads me to wonder, what can I do? Sure, after reading the Ars-technica article I "upped the ante" and went for 11 character per-site passwords without dictionary words in them. But is it enough? Recently, I was troubleshooting an infected Windows 7-laptop, to notice it had Firefox-addons with the same name as a virus. It was then, when I found out that programs can install addons and search bars from _outside_ the browser. What happened to "only install addons from trusted locations?" I tried to find out how I can block addons from beyond the trusted Mozilla-website, but to no avail. I also tried to find out if it was possible to disable all addons and only whitelist a few I trust. Disabling all addons came close, but no cigar. Untrustworthy repositories - the twenty-tens nightmare?This brings me to the next topic: It's really easy to add PPA's in Ubuntu. When discussing the mentioned "lazy-Google" flaw regarding Android-Linux, one might say "But that's only if you use the unofficial repository, usually a Chinese one with pirated Android-Packages (apk's). And you're south of dumb and insanity if you use those, everybody knows they're full of malware". So would I say, in fact. But isn't that hypocritical?As using unofficial untrustworthy repositories is - as far as I know - exactly what PPA's are? It would only take 1 clever attacker to make a seemingly "I want to have it!!" Ubuntu killer app and put it in his PPA to take control over those who are dumb enough to add said PPA. Maybe that's the kind of "social engineering" the seller of the Hand-of-Thief kit was aiming at when asked about the "attack vector". Of course, this goes for most distro's : In Debian, it's easy to add sources to the list, Fedora I think makes it easy to install RPM's found on the web, and also Gentoo always had overlays and even other ways to install "unauthorized" stuff. What's next? Will Canonical and RedHat have to build a white- and blacklist of repositories? It seems after all, the whole idea of one trusted repository isn't that bad. Sadly, however, lots of efforts by the Linux-community is wasted on replicating the efforts and maintaining multiple repositories. Because of all the duplicate work, there are not enough people to test / include all "offered" packages in mainline, which is exactly why people have "personal overlays" and PPA's, a long Debian Sources.list or hunt for RPM's to "click and install". I've seen it happen in Gentoo: It sometimes takes ages before a straightforward version bump is in the official repository, so people start to use other less official and less safe ways. Firefox has the same issue: Usually, you want some addons to make your life easier. However, because it's so easy to install an addon, if I were a malicious attacker, I'd try to write a Firefox-addon which steals bank credentials. I don't need root-access to do so, Firefox access at the user level is enough. That it's possible these days to install Addons in Firefox bypassing Mozilla's Addon website was quite a shock to me. OK, it was a Windows-box, and it happened when I tried to install a .exe I found on the web, but when the installer asked if it was allowed to install a Firefox-addon, I'm pretty sure I said "No". However, after opening Firefox, I still found the new "search engine" (can I say: "Advertizement banner") installed - and also turned on "as default search engine". I hoped this was only IE, but Firefox is turning into this hell as well: 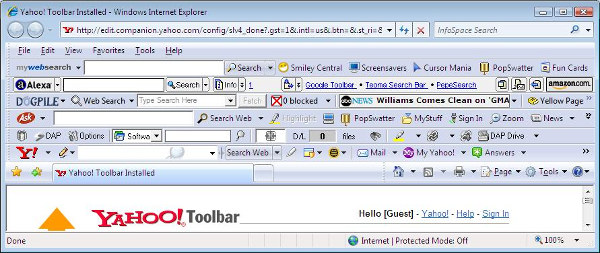 Maybe, after all, Linux-critics might be right: Once more people use Linux, more attackers will try to write malware and exploits for it. I always denied it, but am ready to change my mind. Gradually, running Xombrero on an OpenBSD-image in VirtualBox for e-banking doesn't seem as such a bad idea anymore. In the mean time, I might be investigating ways to "harden Ubuntu" in other ways. Actually, I started using Ubuntu because I wanted to spend less time managing the operating system - like I did in Gentoo (emerging whole day!)- and spending more time actually doing usefull stuff for AFK-life. But bummer, guess what: Actually spending time to manage the OS seems to be necessary these days. Avoiding user friendly solutions such as Ubuntu and Firefox and using NoScript may actually have merit - from a security point of view. Remembering those lucky days!It remembers me of the days when I used AES-encryption with a 32-character keyphrase and feeding arguments manually to the dm-mapper, finding out why my hardened-Gentoo - of course with SE Linux enabled - didn't want to run certain programs using strace and trying to understand the Backus-Naur notation of man sudo. And later manually adding lots of whitelist-websites to NoScript. All of that in the cold winter. Without having eaten and no food in the house. With consecutive hours of rain outside. With a sore bum on a mediocre second hand chair. After midnight. In the dark. Alone.So, here's my question to you: Are you afraid attackers break into your Linux boxes? Do you sniff and snort- ehr, your network, that is? Do you scan for rootkits from time to time, and check md5-sums of executables against your "trusted-list"? Do you consider one distro safer as another? What is your level of paranoia? Is the alu-foil within reach?  |
 LXer Feature: 13-August-2013
Comments (40)
20 earlier comments in the full thread.
> Debian: The Distribution on Everyone's "maybe" List.
Debian is that slightly outdated pack of blueberry yoghurt that you can still eat in case you're too lazy going to the store and there's nothing else left in the fridge.
Debian is that slightly outdated pack of blueberry yoghurt that you can still eat in case you're too lazy going to the store and there's nothing else left in the fridge.
I regularly eat out-of-date yogurt, and it's totally fine.
Hmm, I never had good experiences with Debian, I'm afraid Debian doesn't like me. Just like the yoghurt, it shouldn't remain unattended for too long. I mean, I give it the task to install say 30 packages, and then it asks all kind of stupid questions about programs you never chose to install in first place. Last time I looked, bringing in certain 'server'-programs as a dependency if you're not going to use those server-programs is not a good idea from a security standpoint. That's why I like Gentoo, compiling everything and distinguishing fires of programs who don't like each other is such a nightmare and tedious task, that you strip out everything you don't use.
I think my last-resort option in the fridge security-wise is BSD. The right turning variant.
OK, it also has some servers configured by default, but at least it doesn't ask you questions about servers you don't know yet, and it and just makes the safe choices for you. Besides, at least OpenBSD is much easier to install than _any_ Linux (and also FreeBSD) in my experience.
Wow, lots of misinformation, jazz. Let's start with your stats: most corporate servers are behind firewalls and can't be counted on the web at all. Debian has a significant presence in hosting companies as I've said before and that is what you are seeing. Do me a favor: look at any tech job board and tell me how many jobs there are for Red Hat, SUSE, Debian and Ubuntu. On a good day Debian and Ubuntu might add up to one in my area, while Red Hat has dozens. Web stats are totally useless for measuring the corporate market.
Also, Fedora is not Red Hat Enterprise Linux at all. It's the test bed masquerading as some sort of community distro. (There are community bits and pieces, but Red Hat's interest is as a test bed.) When I talk about free Red Hat clones I mean CentOS, Scientific Linux and Springdale Linux, not Fedora.
Red Hat Enterprise Desktop and Workstation use GNOME 2, not GNOME 3. I'll also put it to you that GNOME 3, as it exists today (not when it came out) is a decent desktop. Have you tried it lately, as in a really new version with the ability to operate like GNOME 2? Your confusing Fedora with Red Hat again, and they are about as similar as ice cream and turnips. Yes, both are foods. The comparison ends there.
For Red Hat and clones the EPEL (Extra Packages for Enterprise Linux) repository, maintained by the Fedora project (which is owned by Red Hat) adds the missing software quite nicely for most things. No need at all to go to miscellaneous repos in most cases. Others (like Atomic) have corporate backing and can be purchased with support and guarantees or used freely, your choice.
Ubuntu's support cycle (including LTS) is just way too short for most businesses. The main 9 month cycle is insane and has basically turned Ubuntu into a toy.
Quoting:The french police force (Gendarmerie Nationale) is running Ubuntu LTS on their 90.000 desktop clients. Ubuntu Server LTS is also used by Online.net (a.k.a. Free.fr), one of France's biggest access provider and webhosting company.How nice for France. However, since my comment said: "For the enterprise that's it AFAICT in North America." it's kind of irrelevant.
irrelevant, adj.: 1) any technical decision not made by Caitlyn Martin 2) any Linux distribution not used by Caitlyn Martin 3) any country not inhabited by Caitlyn Martin 4) any political view not shared by Caitlyn Martin 5) more generally, any person not being Caitlyn Martin.
Quoting:Let's start with your stats: most corporate servers are behind firewalls and can't be counted on the web at all. Debian has a significant presence in hosting companies as I've said before and that is what you are seeing.
At least we're getting somewhere. We both agree there are more Debian & Ubuntu web servers out there than CentOS and RedHat. Do you have any statistics to substantiate your other claims? anything published? articles? maybe some blog posts? Google has difficulties finding them.
Quoting:Do me a favor: look at any tech job board and tell me how many jobs there are for Red Hat, SUSE, Debian and Ubuntu.
If it was so obvious, why aren't more people talking about it? Google must be broken.
Quoting:Red Hat Enterprise Desktop and Workstation use GNOME 2, not GNOME 3.
I guess everybody knows that, and it doesn't mean anything as far as this discussion is concerned. You are off topic.
Quoting:Also, Fedora is not Red Hat Enterprise Linux at all.
Off topic again. Who said Fedora and RHEL are the same thing?
Quoting:It's the test bed masquerading as some sort of community distro. (There are community bits and pieces, but Red Hat's interest is as a test bed.)
Who cares? I definitely don't. They can call it whatever they want. It is like the TV commercials.
Quoting:I'll also put it to you that GNOME 3, as it exists today (not when it came out) is a decent desktop. Have you tried it lately, as in a really new version with the ability to operate like GNOME 2?
It failed to get any kind of traction with the large public, this is why they reverted to classic mode. It is a monumental failure, they spent 3 years developing it, and it was for nothing.
Gnome 3 doesn't come close to Gnome 2. It has less features than even XFCE or LXDE. Nobody in his right mind will run his business on Gnome 3. RedHat figured that out, people will not pay for Gnome 3, this is why they brought in Mate in F19.
Quoting:Ubuntu's support cycle (including LTS) is just way too short for most businesses.
I would not presume to know what is short or what is not short for businesses. 12.04 is supported until 2017, I think it is reasonable. https://wiki.ubuntu.com/LTS
> We both agree there are more Debian & Ubuntu web servers out there than CentOS and RedHat.
I doubt that's true. I'd guess that at best it's a 50/50 split. Anyone have any actual studies to point to giving the actual percetages?
I doubt that's true. I'd guess that at best it's a 50/50 split. Anyone have any actual studies to point to giving the actual percetages?
The only numbers I have are sales numbers, and, of course, they show Red Hat way out front because you don't buy Debian. However, contrary to jazz's claim, I gave a very clear way to substantiate what I said, which is to look at tech job boards. Now, try looking at them directly, rather than through Google and you will see precisely what I mean.
The rest kind of falls to the level of trolling and baiting. jazz said that Red Hat has no desktop unless you count GNOME 3 and I pointed out that Red Hat doesn't use GNOME 3. Suddenly that's "off topic". Hmmm... I talked about Red Hat, jazz responded with facts about Fedora, I pointed out that Fedora is not Red Hat and then jazz asks who ever claimed they were the same. Hmmm.... As far as presuming what's long enough for business, Red Hat went to ten years support because seven was just too short. SUSE did the same. I'm not presuming, but the real enterprise distros certainly are. It's called customer feedback. Five years simply does not cut it in the joke.
kikinovak: Sorry to tell you this, but despite what French people think, France is not the center of the universe and it is irrelevant to the North American market. I realize anytime I don't post a Slackware commercial it bothers you, but, sorry, some of us have to live in the real world.
OK, we are discussing security here, at least this is the subject of the article. So, according to caitlyn, RedHat is the most secure distro in the world because:
1. RedHat makes lots of $$$
2, If there are jobs, who cares about statistics.
3. Gnome 3 is a desktop.
4. RHEL is supported for 10 years.
5. French people are whatever...
This is supposed to make RHEL a very secure distro, and her arguments are definitely on topic.
1. RedHat makes lots of $$$
2, If there are jobs, who cares about statistics.
3. Gnome 3 is a desktop.
4. RHEL is supported for 10 years.
5. French people are whatever...
This is supposed to make RHEL a very secure distro, and her arguments are definitely on topic.
>The only numbers I have are sales numbers, and, of course, they show Red Hat way out front because you don't buy Debian.
The perennial problem for community distros. :( I expect Debian has a significant market share, even in businesses, but I have no idea what the percentage might be, or how to determine it.
The perennial problem for community distros. :( I expect Debian has a significant market share, even in businesses, but I have no idea what the percentage might be, or how to determine it.
Caitlyn: When the peacock spreads its feathers, what do you see in the middle of all this colorful glory?
@admin: Does this forum have a functionality to filter out selected posters? While I do enjoy reading most of the articles and posts on LXer, I'm growing tired of Miss Caitlyn Martin's toxic rants. I fear this won't stop until every single reader on LXer a) switches to RHEL b) activates SELinux c) despises Slackware for its lack of seriousness and d) agrees Edward Snowden should be court-martialled for high treason. Chances this happens anytime soon are rather thin.
Kiki, yer best score file is yer brain. ;)
Bringing this back on topic, I've come to realize that the biggest security issue is going to be the individual user. Yes, tools such as SELinux exist, but like Kevin Mitnick has argued, social engineering can bypass those measures, hence it's important to train the user to defend against suspicious activity and conversations (i.e. never give passwords or other crucial information over the phone, etc... etc...).
Working in a school or a college is an excellent security training for any sysadmin. Once you've setup a network for hordes of 16-20-year-olds, I guess you can brace yourself for any malevolence under the sun. Their chief concerns are usually a) watching and downloading porn b) get receipts for some homegrown weed c) bypass the Internet filter d) hack the teacher's accounts and delete their data e) hack into the online platform to change their test results f) deface their buddies' accounts with Justin Bieber and/or hardcore porn background images g) download mobile phone ringtones over the school's internet connection so the school has to pay, etc. etc.
After this job, I guess I'll take a project with the russian mafia for relaxing :o)
After this job, I guess I'll take a project with the russian mafia for relaxing :o)
> After this job, I guess I'll take a project with the russian mafia for relaxing :o)
It probably pays better. :)
It probably pays better. :)
Quoting:> After this job, I guess I'll take a project with the russian mafia for relaxing :o)
It probably pays better. :)
But, beware the retirement plan may be short.
Quoting:How nice for France. However, since my comment said: "For the enterprise that's it AFAICT in North America." it's kind of irrelevant.
True, and totally off topic, but nonetheless, however irrelevant, still interesting to see how this is different from region to region.
To test said hypothesis, I just searched a few job forums in NL / FR / IT / DE / UK, and guess what: For the first four, there's more jobs for Debian / Ubuntu (those two combined) listed than for Red Hat, while in the UK it's close.
Post a comment
A free account is needed to post. Write your comment here first: your text is kept in this browser while you sign up or log in, and is waiting for you when you come back.
Your message:Markdown: **bold**, *italic*, [text](https://link), - lists, > quotes, $x^2$ for math. Formatting help
Sign up and post (it is free) or Log in and post

|
|
But Fedora can be set up for multimedia -- I have the RPM Fusion, Adobe and Google repositories in there to bring in the various bits (codecs and proprietary drivers; Flash; and the Chrome browser and Talk plugin, respectively).
Unfortunately my hardware "likes" Fedora more than anything else at the moment. However much you might hate the new Anaconda installer, it "understands" EFI better than anything else out there (or at least in terms of my HP laptop).